
We are issuing an urgent advisory regarding two critical remote code execution (RCE) vulnerabilities affecting the core PHP runtime. All customers must update their PHP installation immediately.
What's happening
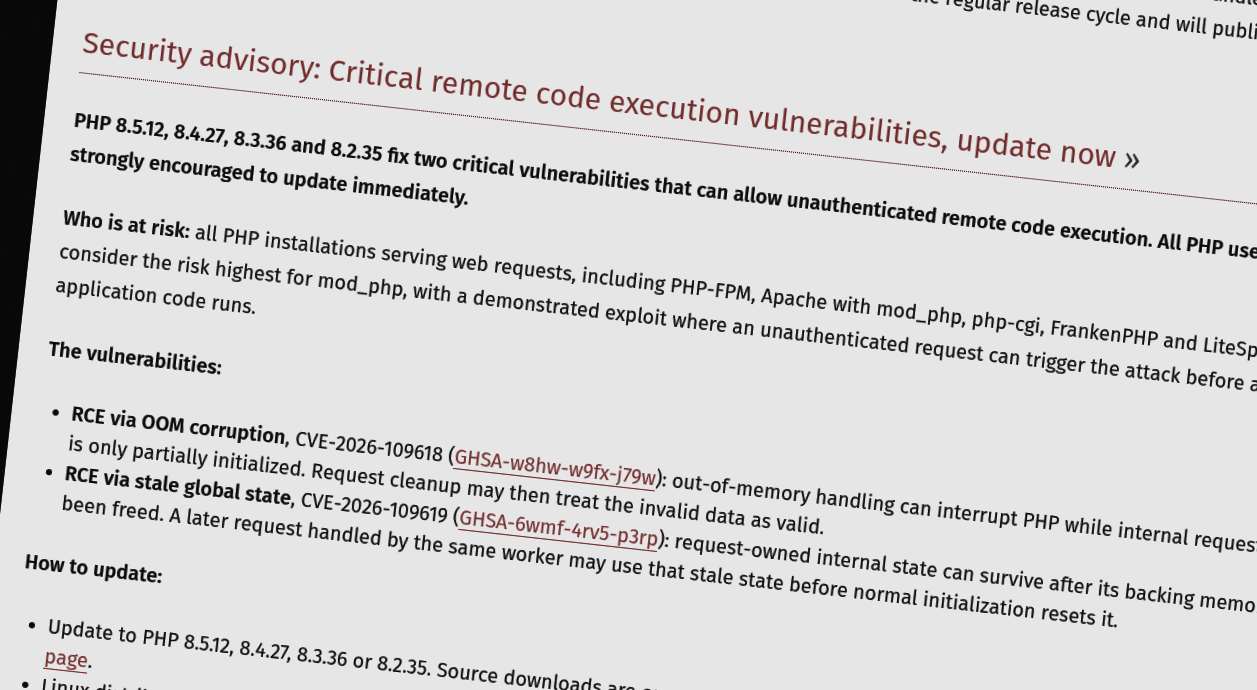
The PHP Foundation has released an emergency out-of-band patch for two critical vulnerabilities in PHP's core request-parsing code:
- CVE-2026-109618 - Out-of-memory corruption leading to RCE (CVSS 9.2)
- CVE-2026-109619 - Use-after-free from stale global state leading to RCE (CVSS 9.2)
Both allow an unauthenticated attacker to run arbitrary code on your server, bypassing application-level code entirely. Because these flaws live in PHP's server-level runtime, they cannot be fixed from within Contentteller, this is a server-level update.
Attacks are already being observed in the wild. Industry analysts expect mass exploitation to begin within minutes of patch release.
What you need to do
Update PHP to a fixed version immediately:
| PHP 8.5 | 8.5.12 |
| PHP 8.4 | 8.4.27 |
| PHP 8.3 | 8.3.36 |
| PHP 8.2 | 8.2.35 |
If you're on PHP 8.2: this is your last security fix before end-of-life (December 31, 2026). Upgrade now.
If you're on 7.4, 8.0, or 8.1: these branches received source backports. Treat yourselves as potentially exposed and upgrade.
If you're on Debian or Ubuntu: Sury.org offer backports with the security fix for PHP 5.6 to 8.5.
Mitigation is not a substitute for patching
No configuration change fully protects you. The following only narrow the attack surface:
- For the OOM bug: set memory_limit=-1 (enforced) and lower post_max_size.
- For the stale-state bug: disable session.upload_progress; on PHP 8.5, set fatal_error_backtraces=0.
None of these make you safe.
Verify your version
Running php -v via the CLI can report a different version than your web layer actually uses. We'll verify the effective version through the real web SAPI.